Every action is attributable.
Every claim is checkable.
Access reviews, legal holds, backups and audits run on the same record as the work, so evidence is something you export, not something you assemble.
 Access review · Fieldbook CRMShare
Entra ID, Okta or SAML, with MFA enforced and one permission console.
Every change is chained, so tampering shows and history is provable.
A hold blocks every purge path for the records it covers.
One record. Every desk it crosses.
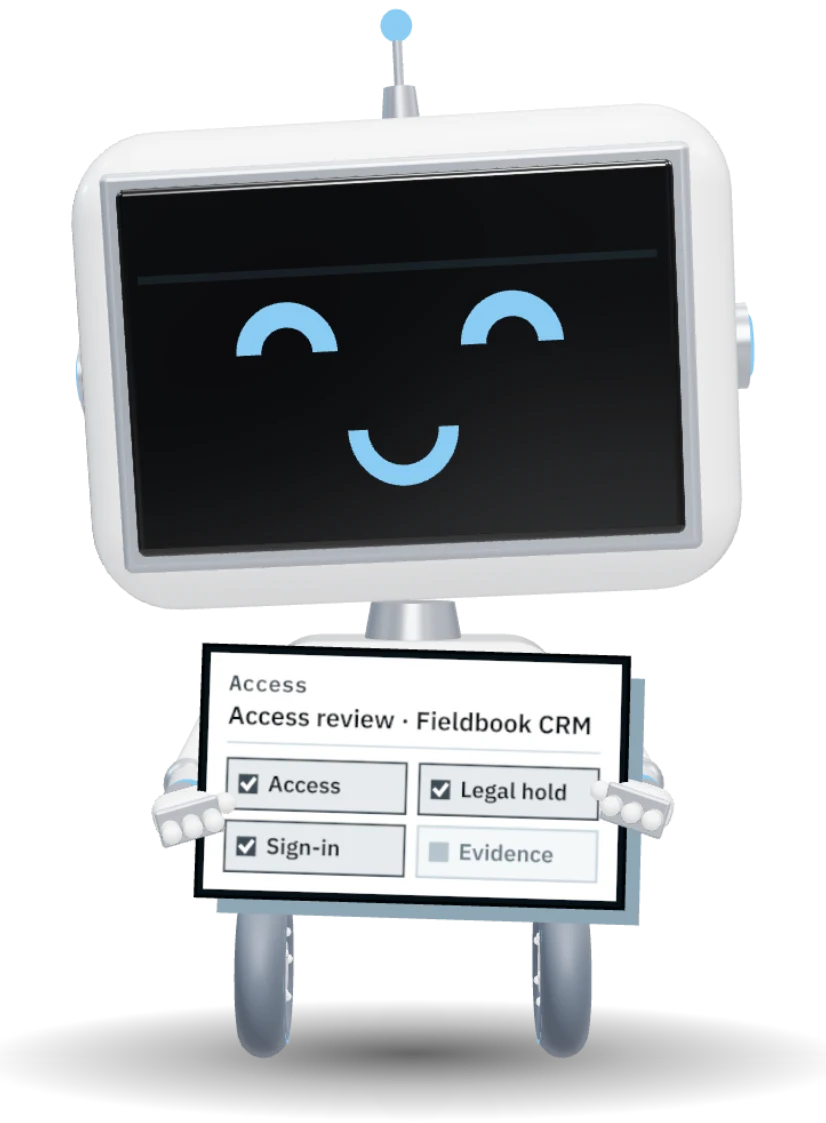
Opens the quarterly access review
30 min savedRevokes seven users in one pass
60 min savedPlaces a legal hold on a supplier dispute
45 min savedConfirms MFA is enforced everywhere
20 min savedDownloads the evidence pack and verifies the chain
120 min savedThe right people.
Nobody else.
One capability map, shown to you.
Sign in with Entra ID, Okta or any SAML provider, with MFA enforced. Roles map to capabilities in one place, and the permissions console shows exactly who can do what.
- Every state-changing route checked for authorization, swept in automated tests
- Every admin route refused to ordinary users, tested on every build
- Bulk actions ask the same question per row as the single action
Fails closed.
Says why.
The defaults are the safe ones. When something refuses, it tells you.
Email replies need proof
A reply by email only updates a ticket when the sender is verified. Otherwise it becomes an internal note.
AI stays on the box
Run models on your own GPU. Sending content to a cloud model needs explicit egress consent and a key.
Licenses never lock you out
An expired license never blocks sign-in, password reset, MFA or SSO, and never blocks business work.
Headers and CSP
Strict security headers and a content security policy on every response, scanned with DAST.
Failures are recorded
A panel that cannot load records why in Diagnostics, instead of rendering blank.
Export everything
Any module exports its data in any state, including when it is switched off.
Kept as long as you need.
Proven when you need it.
Hash-chained audit trail
Every change chained to the last, so tampering shows. An auditor evidence pack exports it.
Legal holds
A held record or document cannot be purged by any path, manual or scheduled.
Retention rules
Every log has a stated retention window you set, pruned in batches, with stalls reported.
Archive, not delete
Closed records archive and stay in search, reports and totals.
Encrypted backups
AES-256 archives shipped off-box, with a monthly restore drill that proves they work.
Every action attributed
Who did it, when, from where, and what it was before.
Walkthrough · your process PNMCLOShareBring your security questionnaire.
We will answer it on the call, in the product, against the running build.